
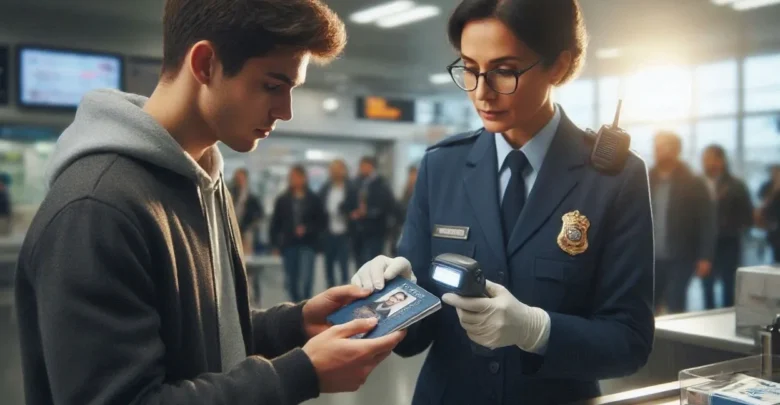
Border systems use trusted public key certificates to verify the issuer’s signature and check the integrity of electronic records.
WASHINGTON, DC, October 15, 2026 — When an electronic passport issued by one country arrives at another country’s border, the receiving authority must determine whether the information stored inside that document can be trusted even though the passport originated from a completely separate national issuance system.
Digital signatures and public key certificates help solve that international trust problem by allowing compatible inspection systems to cryptographically link protected passport information to credentials associated with the issuing authority and verify that those records remain unchanged after legitimate personalization.
Electronic Passports Need a Cross-Border Trust Mechanism
International travel would become much more difficult if every border officer had to contact the issuing government whenever a foreign electronic passport appeared, especially since major airports routinely process documents from dozens or even hundreds of jurisdictions.
Public key infrastructure provides a scalable alternative by letting governments distribute verification credentials that foreign authorities can use to examine digitally signed passport information without accessing the confidential private keys used during the original document-signing process.
The ICAO electronic passport security framework sets technical specifications for the public key infrastructure that supports electronic machine-readable travel documents, including certificate structures and the cryptographic relationships used during international verification.
The Issuing Authority Creates the Digital Signature
During electronic passport personalization, the Issuing Authority associates protected information stored in the chip with a digital signature created using cryptographic credentials controlled by the issuing state or organization responsible for producing the travel document.
That signature provides receiving inspection systems with mathematical evidence that can later be evaluated using the corresponding public key information, allowing authorities to determine whether the protected electronic data retain the relationship established during legitimate government issuance.
Digital signatures are particularly valuable because they can reveal unauthorized electronic alteration even when changed identity information appears visually convincing after being retrieved from the chip and displayed on an inspection terminal.
Private and Public Keys Perform Different Functions
The issuing authority protects a private signing key within its secure passport infrastructure, while the corresponding public key can be distributed to foreign authorities that need to verify signatures created during legitimate document production.
This separation lets another country verify a signature without receiving the cryptographic capability needed to create new signatures that inspection equipment could mistakenly accept as originating from the passport issuer.
The architecture therefore supports international authentication while preserving national control over the highly sensitive signing credentials used to protect electronic passport information during issuance.
Document Signer Certificates Support Passport Verification
Electronic passport systems commonly use Document Signer Certificates, which link the public key used to sign passports to the broader certificate hierarchy maintained by the issuing state or a recognized organization.
When a foreign inspection system encounters an electronic passport, it can examine the relevant signer certificate and determine whether it can link that certificate through an appropriate trust path to credentials already recognized for the issuing authority.
ICAO specifies that electronic machine-readable travel document public key infrastructure supports verifying signed objects such as the Document Security Object, with signer certificates digitally signed by the issuing state’s Country Signing Certification Authority.
The Country Signing Authority Provides a Higher Trust Point
The Country Signing Certification Authority, commonly abbreviated CSCA, sits higher in the electronic passport certificate hierarchy and provides an important national trust point for validating Document Signer Certificates for passports issued under that authority.
A receiving country therefore does not simply trust whatever signer certificate appears alongside passport data, because the inspection system must determine whether that certificate ultimately connects with a CSCA credential that the receiving authority already recognizes as legitimate.
This hierarchical structure helps prevent an unknown party from generating its own certificate, labeling it as belonging to a foreign government, and expecting compatible border systems to accept the resulting passport signatures automatically.
Certificate Chains Establish the Relationship With the Issuer
During validation, inspection software can build a certificate path from the signer responsible for the passport data to a trusted certificate associated with the country that issued the travel document.
The inspection system then evaluates whether those certificates remain valid for the relevant purpose, whether the required cryptographic relationships are correct, and whether information identifying the issuing country remains consistent across the certificate and passport data.
Current ICAO inspection guidance recommends checking consistency among the country information in the Document Signer Certificate, the trusted CSCA certificate, electronic passport data, and the visually printed machine-readable zone.
Passive Authentication Uses Those Trusted Credentials
Passive authentication is the process by which an inspection system evaluates the signed security information stored in an electronic passport and determines whether the protected data remain consistent with what the issuing authority originally signed.
The reader first needs confidence in the signing certificate, because verifying a mathematical signature provides little security if the system cannot determine whether the certificate used for that verification genuinely belongs to the government identified as the issuer.
Once the inspection system has established the trusted public key, it can evaluate the signature protecting the passport’s Document Security Object and compare protected reference values with information currently stored in the chip.
Integrity Checks Help Detect Electronic Tampering
Cryptographic hash values stored in the signed security structure can represent protected passport data groups, allowing the inspection reader to calculate fresh values from the information retrieved from the passport.
If an unauthorized party changes protected biographical information or substitutes the digital facial image after legitimate issuance, the recalculated value should no longer correspond with the signed reference information established during passport personalization.
Digital signatures therefore help receiving countries evaluate both origin and integrity, providing evidence that electronically stored information remains connected with the issuing framework and has not been silently modified after the document entered circulation.
Foreign Border Systems Need Trusted Public Certificates
The difficult international question is not how a computer mathematically verifies a digital signature, but how a receiving government obtains trustworthy public certificates for passport issuers worldwide.
Countries can exchange certificate information through recognized diplomatic and technical channels, allowing border authorities to establish trusted national credentials independently of whatever information an individual passport presents.
This independent trust distribution prevents the passport itself from becoming the sole authority for deciding which certificate to trust when border authorities examine its electronic information.
The ICAO Public Key Directory Supports International Exchange
The ICAO Public Key Directory was established to facilitate the international exchange of public key information used for electronic passport validation, reducing the complexity of individual governments maintaining numerous separate bilateral certificate-distribution arrangements.
ICAO describes the directory as a central mechanism that supports the multilateral exchange of information needed to validate electronic passport digital signatures, helping participating border authorities more efficiently access trusted certificate material during international inspections.
The system distributes cryptographic trust information rather than serving as a global repository of identity records, photographs, passport numbers, or travel histories for everyone carrying an electronic passport.
The PKD Helps Scale International Passport Authentication
Before centralized certificate exchange, countries relied more on bilateral diplomatic distribution of signing certificates, an approach that became increasingly complicated as electronic passports spread across more issuing states.
ICAO documentation records that inconsistent bilateral exchange practices created inefficiencies and encouraged the development of mechanisms to distribute issuing-state public keys more effectively, including methods associated with the international Public Key Directory infrastructure.
A shared trust-distribution environment therefore improves scalability because each participating authority can obtain relevant cryptographic information through recognized channels rather than negotiating a completely independent technical exchange relationship with every foreign issuer.
Certificate Trust Must Be Maintained Over Time
Passport signing credentials do not remain unchanged forever, because issuing authorities periodically replace keys, issue new Document Signer Certificates, publish revocation information, or update other cryptographic components as part of normal security management.
Receiving countries therefore need systems that maintain current trust information while also recognizing legitimate passports issued under earlier certificates that can remain valid for years after a newer signing credential enters service.
The ICAO Public Key Directory continues to distribute current electronic machine-readable travel document certificate collections and related objects, showing how international passport authentication depends on continuously maintained trust information rather than a single permanent certificate issued indefinitely.
Revocation Information Can Change What a Border System Trusts
A certificate that was once legitimate may later require revocation as security circumstances change, so inspection infrastructure needs mechanisms to identify credentials the responsible authority no longer considers suitable for continued trust.
Certificate Revocation Lists can communicate this information within the electronic passport public key infrastructure, allowing inspection systems to account for changes affecting previously issued cryptographic credentials rather than assuming every historically valid certificate remains acceptable forever.
ICAO’s current public key infrastructure specifications address revocation information within certificate management, reflecting the importance of maintaining trust throughout the operational lifecycle of electronic passport signing credentials.
A Valid Signature Does Not Prove Everything About the Passport
Successfully verifying a foreign passport’s digital signature provides important evidence about protected electronic information, but that result does not independently establish that the document remains legally valid, belongs to the person presenting it, or contains an untouched physical booklet.
The issuing government could subsequently report the passport lost, stolen, canceled, or revoked while the original chip data and digital signature remain mathematically unchanged from the day the legitimate document was produced.
Border authorities therefore combine cryptographic verification with separate document-status checks, physical examination, biometric comparison, and immigration procedures instead of treating a successful signature result as a complete border decision.
Physical and Electronic Identity Information Should Agree
Electronic authentication becomes more useful when the foreign passport’s protected data match information printed or laser-engraved on the visible identity page and encoded in the machine-readable zone.
Current ICAO inspection guidance specifically recommends consistency checks involving electronic data, signer certificates, trusted national certificates, and the visual machine-readable zone, creating additional opportunities for authorities to identify unexplained discrepancies.
A valid digital signature protecting one identity, combined with visibly different information elsewhere in the passport, would therefore provide a strong reason for further examination rather than reassurance that the complete document is authentic.
The Facial Image Can Be Used After Electronic Validation
Once an inspection system has established appropriate confidence in protected foreign passport information, the electronic facial image can provide a trusted reference for comparing the document with the traveler physically presenting it.
This biometric comparison performs a fundamentally different task from validating certificates, because public key infrastructure helps establish confidence in electronic document data while facial verification helps determine whether the traveler corresponds with the person represented by that data.
ICAO inspection guidance places biometric verification after relevant electronic document checks, reflecting the importance of obtaining confidence in the passport information before using its portrait as the reference for comparing the holder.
Public Certificates Do Not Reveal the Issuer’s Private Key
Foreign governments can verify passport signatures without weakening the issuing state’s control over its signing system because public key information does not provide the secret private key needed to generate legitimate government signatures.
This asymmetric cryptographic model allows verification capability to be distributed broadly among trusted inspection environments while preserving the critical distinction between authorities permitted to check passports and authorities permitted to create signed passport information.
The arrangement makes international authentication practical because an inspection system in another country can evaluate the mathematical evidence supporting the document without gaining access to the issuing government’s confidential production credentials.
Electronic Verification Depends on Implementation Quality
Even well-designed international standards cannot guarantee reliable authentication if inspection software handles certificates incorrectly, trust stores become outdated, cryptographic algorithms are implemented poorly, or border infrastructure fails to maintain current information.
Receiving governments therefore need more than technically capable passport readers, because operational procedures surrounding certificate updates, revocation information, software maintenance, system security, and trusted distribution channels remain essential parts of the authentication environment.
Electronic passport security therefore depends on both strong cryptographic design and disciplined administration by the governments that operate the issuing and receiving systems.
Different Passport Generations Can Use Different Credentials
Foreign electronic passports can remain valid for many years, so a border authority may encounter multiple legitimate document generations, each with different signing certificates, algorithms, chip technologies, or national passport designs, during the same inspection period.
A system that recognizes only the newest credential risks rejecting legitimate older documents, while one that indiscriminately accepts outdated trust information could weaken the security benefits of carefully managed certificate lifecycles.
Modern inspection environments therefore need enough historical and current trust information to evaluate each passport according to the cryptographic environment applicable when that document was legitimately issued.
Signature Verification Does Not Replace Anti-Cloning Checks
A valid digital signature can show that copied passport data remain unchanged, but it does not necessarily prove that those legitimate data come from the original secure chip associated with the physical travel document.
Additional mechanisms such as Active Authentication or Chip Authentication can address chip substitution or cloning when the passport generation and inspection equipment supports them, while passive authentication continues to protect the integrity of signed electronic information.
This distinction reinforces the broader principle that, even within electronic passport security, different cryptographic checks protect against different attack types, rather than one procedure solving every possible authenticity problem.
Foreign Passport Verification Depends on Shared Technical Language
Public key certificates work internationally because issuing and receiving authorities follow common technical specifications that define certificate structures, signing processes, protected data, cryptographic algorithms, and verification procedures.
Without that standardization, a foreign border system could have the correct public key yet still lack reliable ways to interpret how the issuing country organized or protected the information stored in its electronic passport.
ICAO standards therefore provide the common technical language through which sovereign governments can authenticate one another’s electronic travel documents while continuing to operate separate national issuance systems.
International Trust Remains Sovereign Trust
Global technical infrastructure does not transfer passport-issuing authority to an international organization, because each government remains responsible for deciding who receives its passports and for protecting the private cryptographic credentials associated with those documents.
International certificate exchange simply gives another sovereign government a mechanism to evaluate evidence supporting a foreign passport without gaining control of the system that created the credential.
This distinction lets electronic authentication strengthen international cooperation while preserving the fundamental national authority behind passport issuance and border control.
Digital Signatures Make Foreign Verification More Scalable
The practical strength of public key infrastructure becomes particularly clear at large international airports, where border agencies must evaluate passports issued by numerous countries without delaying routine travelers for direct manual confirmation from every foreign authority.
Digital signatures let the receiving authority verify much of that information locally and quickly once it trusts the certificate, while unusual or unresolved cases can still move to secondary inspection or government-to-government inquiry.
Cryptographic trust therefore provides both a security benefit and an operational advantage by allowing routine authentication to function efficiently across a global travel environment.
Trust Comes From the Certificate Path, Not Appearance Alone
A passport can display sophisticated artwork, a functioning chip, and convincing personal information while still requiring electronic verification because visual appearance cannot establish whether protected data genuinely connects with the foreign issuing authority’s cryptographic credentials.
Similarly, the inspection system cannot simply trust a certificate because it contains an official-looking country name; it must connect that certificate to independently trusted public key information associated with the legitimate issuer.
Security comes from validating the cryptographic path rather than accepting the label attached to the certificate or the travel document’s visual appearance.
Digital Signatures Strengthen International Confidence
Through Amicus International Consulting’s passport security resource, readers can examine how international certificate trust works alongside electronic chips, biometrics, physical security, access controls, and government databases within the broader process of modern passport authentication.
A foreign passport becomes more trustworthy when the receiving authority can verify that protected information remains unchanged and trace the relevant signature through public certificates linked to the recognized issuing government.
Trusted Certificates Connect Foreign Issuers With Border Systems
Digital signatures help establish trust in foreign passports because they let receiving authorities mathematically verify protected electronic information, while public key certificates provide the trusted link needed to associate those signatures with recognized issuing states.
The process does not eliminate the need for physical examination, facial verification, document-status checks, or immigration controls, but it gives border agencies an independent method for assessing whether foreign electronic passport data remain connected with legitimate government issuance.
By combining cryptographic verification with trusted certificate distribution, modern border systems can efficiently authenticate foreign electronic information while letting each issuing country retain exclusive control over the private keys and government processes used to create its passports.